
Security and Trust
Agencies trust SimpliGov with sensitive data and critical processes, protected at FedRAMP High.
Authorization
FedRAMP High
Listing
FedRAMP Marketplace
Independent audit
SOC 2 Type II, unqualified opinion
Regulated data
HIPAA and PCI DSS assessed
Penetration testing
Quarterly, by a third party
fedRAMP High
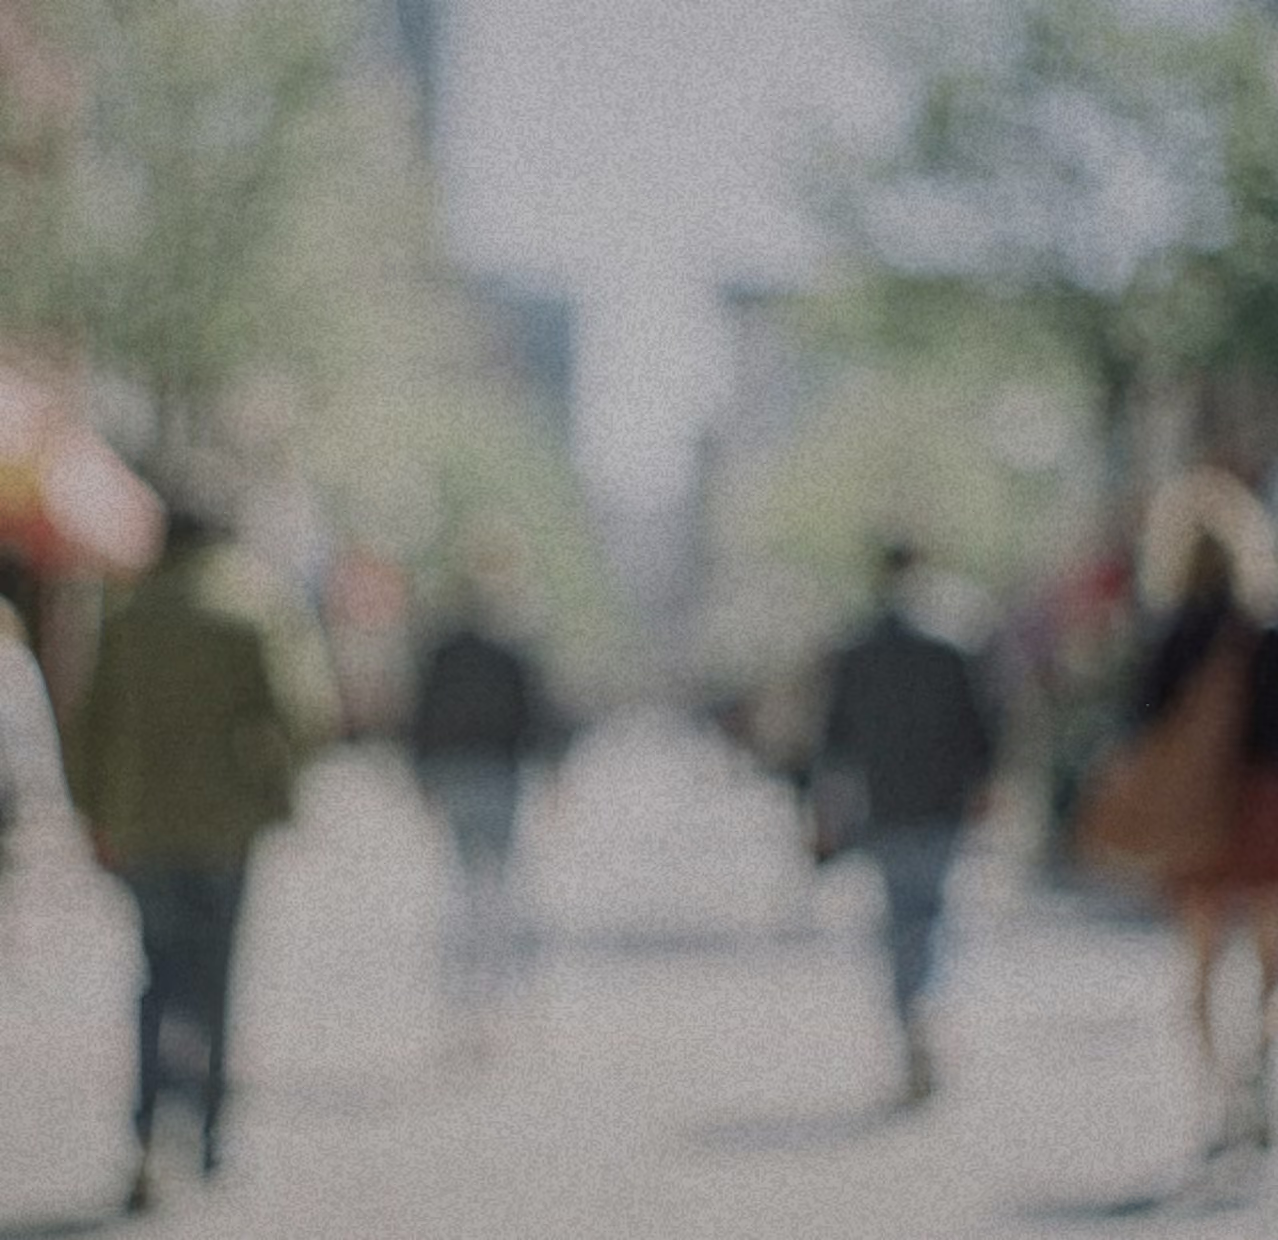
Agencies run on Microsoft Azure Government — U.S. government cloud infrastructure operated separately from Azure commercial — with per-agency data isolation and disaster recovery exercised end to end.


What High means
The most demanding of FedRAMP’s impact levels. Controls come from NIST SP 800-53, the impact level is set under FIPS 199, and High applies to systems holding data whose loss would cause severe or catastrophic harm.c
Independently assessed
Controls are examined by an accredited third-party assessment organization, not self-attested.
Continuously monitored
Authorization is a standing obligation — ongoing vulnerability scanning, reporting, and review of significant changes.
Reusable by agencies
Agencies request the authorization package from FedRAMP by submitting a signed access request and NDA, then build on assessment work already completed rather than starting from scratch.
What it gives you
A credential you can put to work — in renewals, in audits, and in front of your own security and procurement reviewers.
Certifications and audits
FedRAMP High sits alongside the attestations agencies ask for by name. Third-party assessors examine the platform’s controls against each of these standards; the FedRAMP listing is on the Marketplace and the authorization package is released to agencies through FedRAMP’s package access request process; the remaining reports come from your account team under NDA.
The strongest baseline available for cloud services handling unclassified federal data. Assessed by an accredited third-party assessor and monitored continuously, with the authorization package available to agencies through FedRAMP’s package access request process.
Listed on the FedRAMP Marketplace
Tests whether controls operated across a full audit period. Covers security, availability, confidentiality, and processing integrity. Most recent report: unqualified opinion, no exceptions.
Report available under NDA
Assessed as a service provider by a Qualified Security Assessor, full assessment, Compliant rating. SimpliGov never stores or processes a full card number — your payment processor handles card data and we keep only a reference token.
Attestation of compliance
An independent assessment of administrative, physical, technical, and organizational safeguards, plus privacy and breach-notification requirements. Every applicable control assessed effective, no risks identified, overall rating Satisfactory.
Risk assessment on file
Certification scope, audit periods, and assessor details are provided in the reports themselves.
Security Program
Engineering, operations, and support work under the same documented policies — data classification, access control, change management, incident response, disaster recovery — reviewed at least annually, with disaster recovery and incident response tested on a schedule.
Applications & Access
Policies & Procedures
Systems & Operations
Infrastructure & Resilience
Transmission & Storage
Monitoring & Response
SimpliAI
SimpliAI runs in SimpliGov’s Azure Government environment under the same access, logging, and tenant-isolation controls as the rest of the platform. It does not send agency content to commercial models, sees only what a user gives it, and produces drafts that must be reviewed.
Where processing happens
What SimpliAI can see
Your data stays yours
People stay in control
Logging, response, and retention
Your Security Review
These are the documents we provide to procurement and information security reviewers, most of them under a mutual NDA.
The System Security Plan and supporting authorization artifacts, released to agency security teams through FedRAMP’s package access request process.
Availability: Via FedRAMP package request
The full independent service auditor’s report, including the system description, control activities, and the assessor’s tests and results.
Availability: Under NDA
The service provider AOC signed by our Qualified Security Assessor, for agencies processing card payments through the platform.
Availability: Under NDA
Independent assessment of administrative, physical, and technical safeguards against the HIPAA Security Rule, with the accompanying risk assessment control matrix.
Availability: Under NDA
An executive summary of the most recent third-party internal and external penetration test, with remediation status.
Availability: Under NDA
Service commitments, the 98% uptime commitment, service level credits, and support response times by priority.
Availability: Published
Completed responses to standard state and local security questionnaires, prepared by the team that owns the controls.
Availability: On request
Your reviewers can request our FedRAMP authorization package from FedRAMP directly, and we will send the SOC 2 Type II, PCI attestation, HIPAA assessment, and penetration test summary under NDA.